Full-Stack QA Audit for a Supabase-Powered Startup
How we uncovered critical security and performance risks in a fast-growing SaaS platform before their major product launch.
Shipping fast without a safety net
The client was a YC-backed startup building a SaaS platform on Supabase and Astro. With a major product launch approaching, their engineering team was moving fast — but had no formal QA process in place.
They had no regression coverage, no API validation, and had never audited their Supabase security policies. They knew something could go wrong. They didn't know what, or how bad.
They needed a complete picture of their quality posture before going live.
Four issues that would have hurt at launch
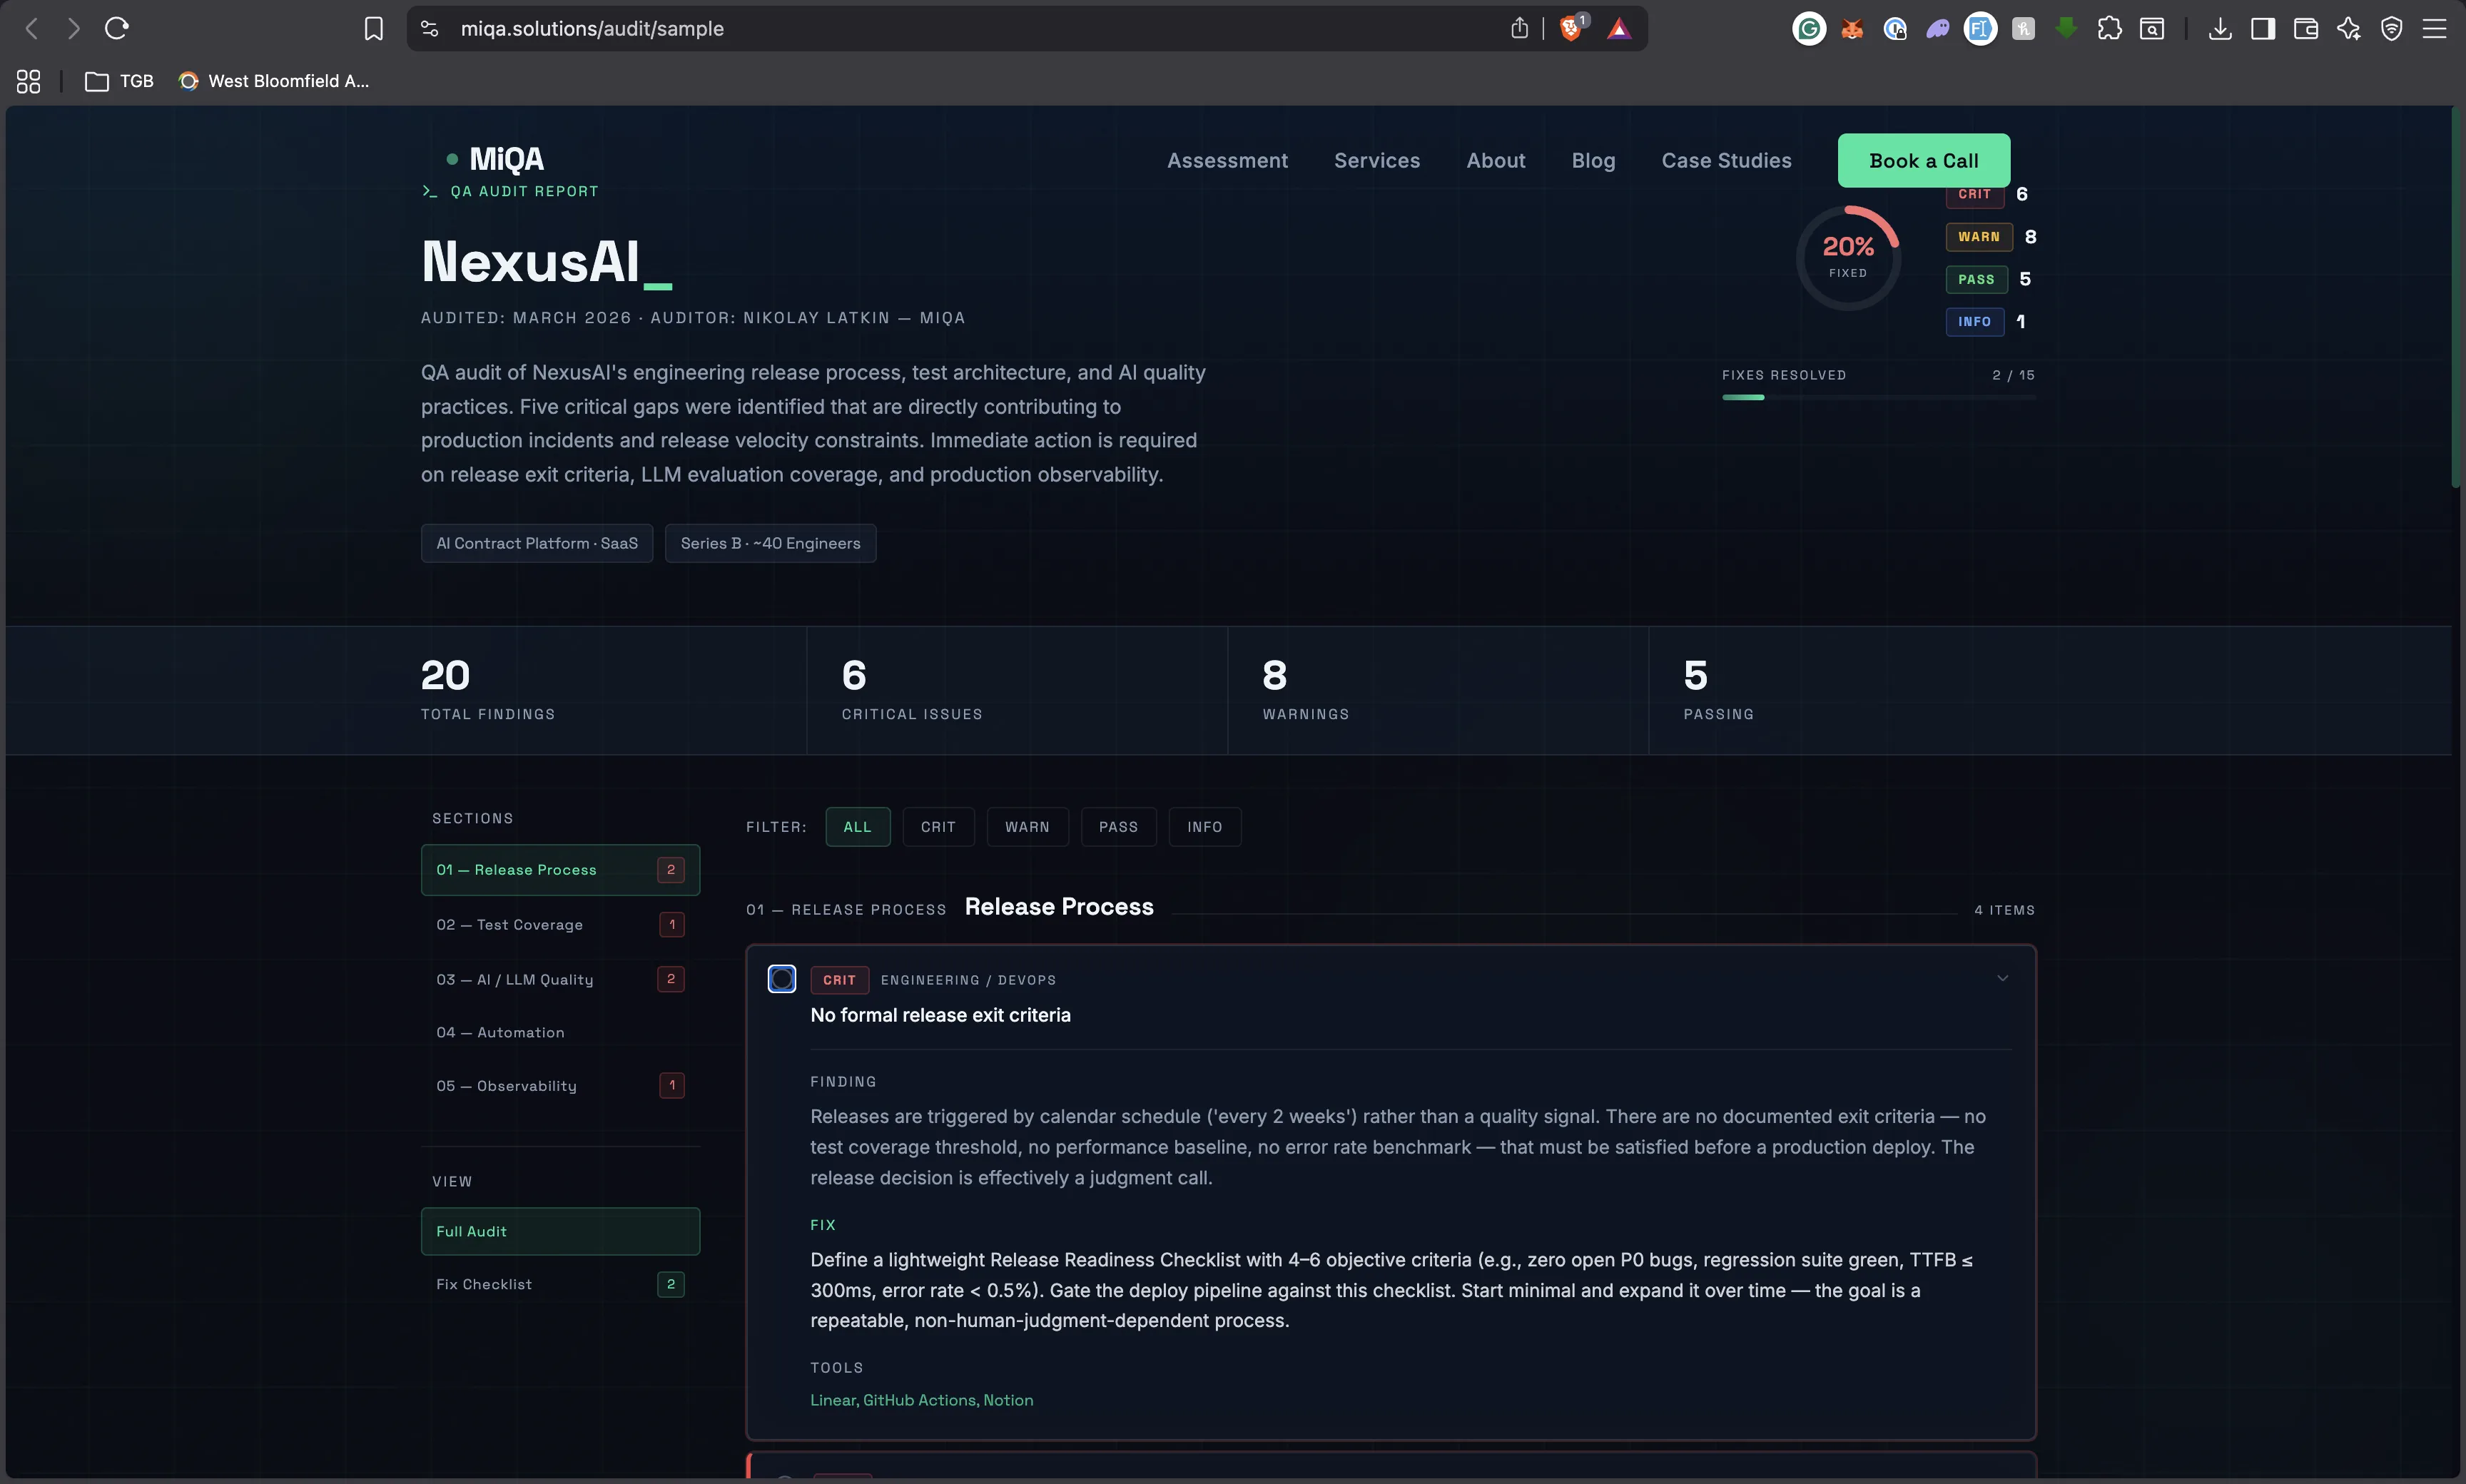
Our 6-step audit covered UI/UX, user flows, API validation, SEO, and Supabase security. Here's what we found:
| Finding | Risk |
|---|---|
| Missing RLS Policy Any user could potentially read data from other users in the assessments table. | Critical |
| API 500 Error (Silent Failure) The save-assessment endpoint failed silently on malformed payloads, causing data loss. | High |
| Broken Blog Posts (66%) Cloudflare Worker error on 2 of 3 blog posts — wasting their content marketing investment. | Medium |
| Relative OG Image URL Social sharing previews broken on LinkedIn and Twitter — reducing distribution impact. | Low |
An interactive dashboard, not a PDF
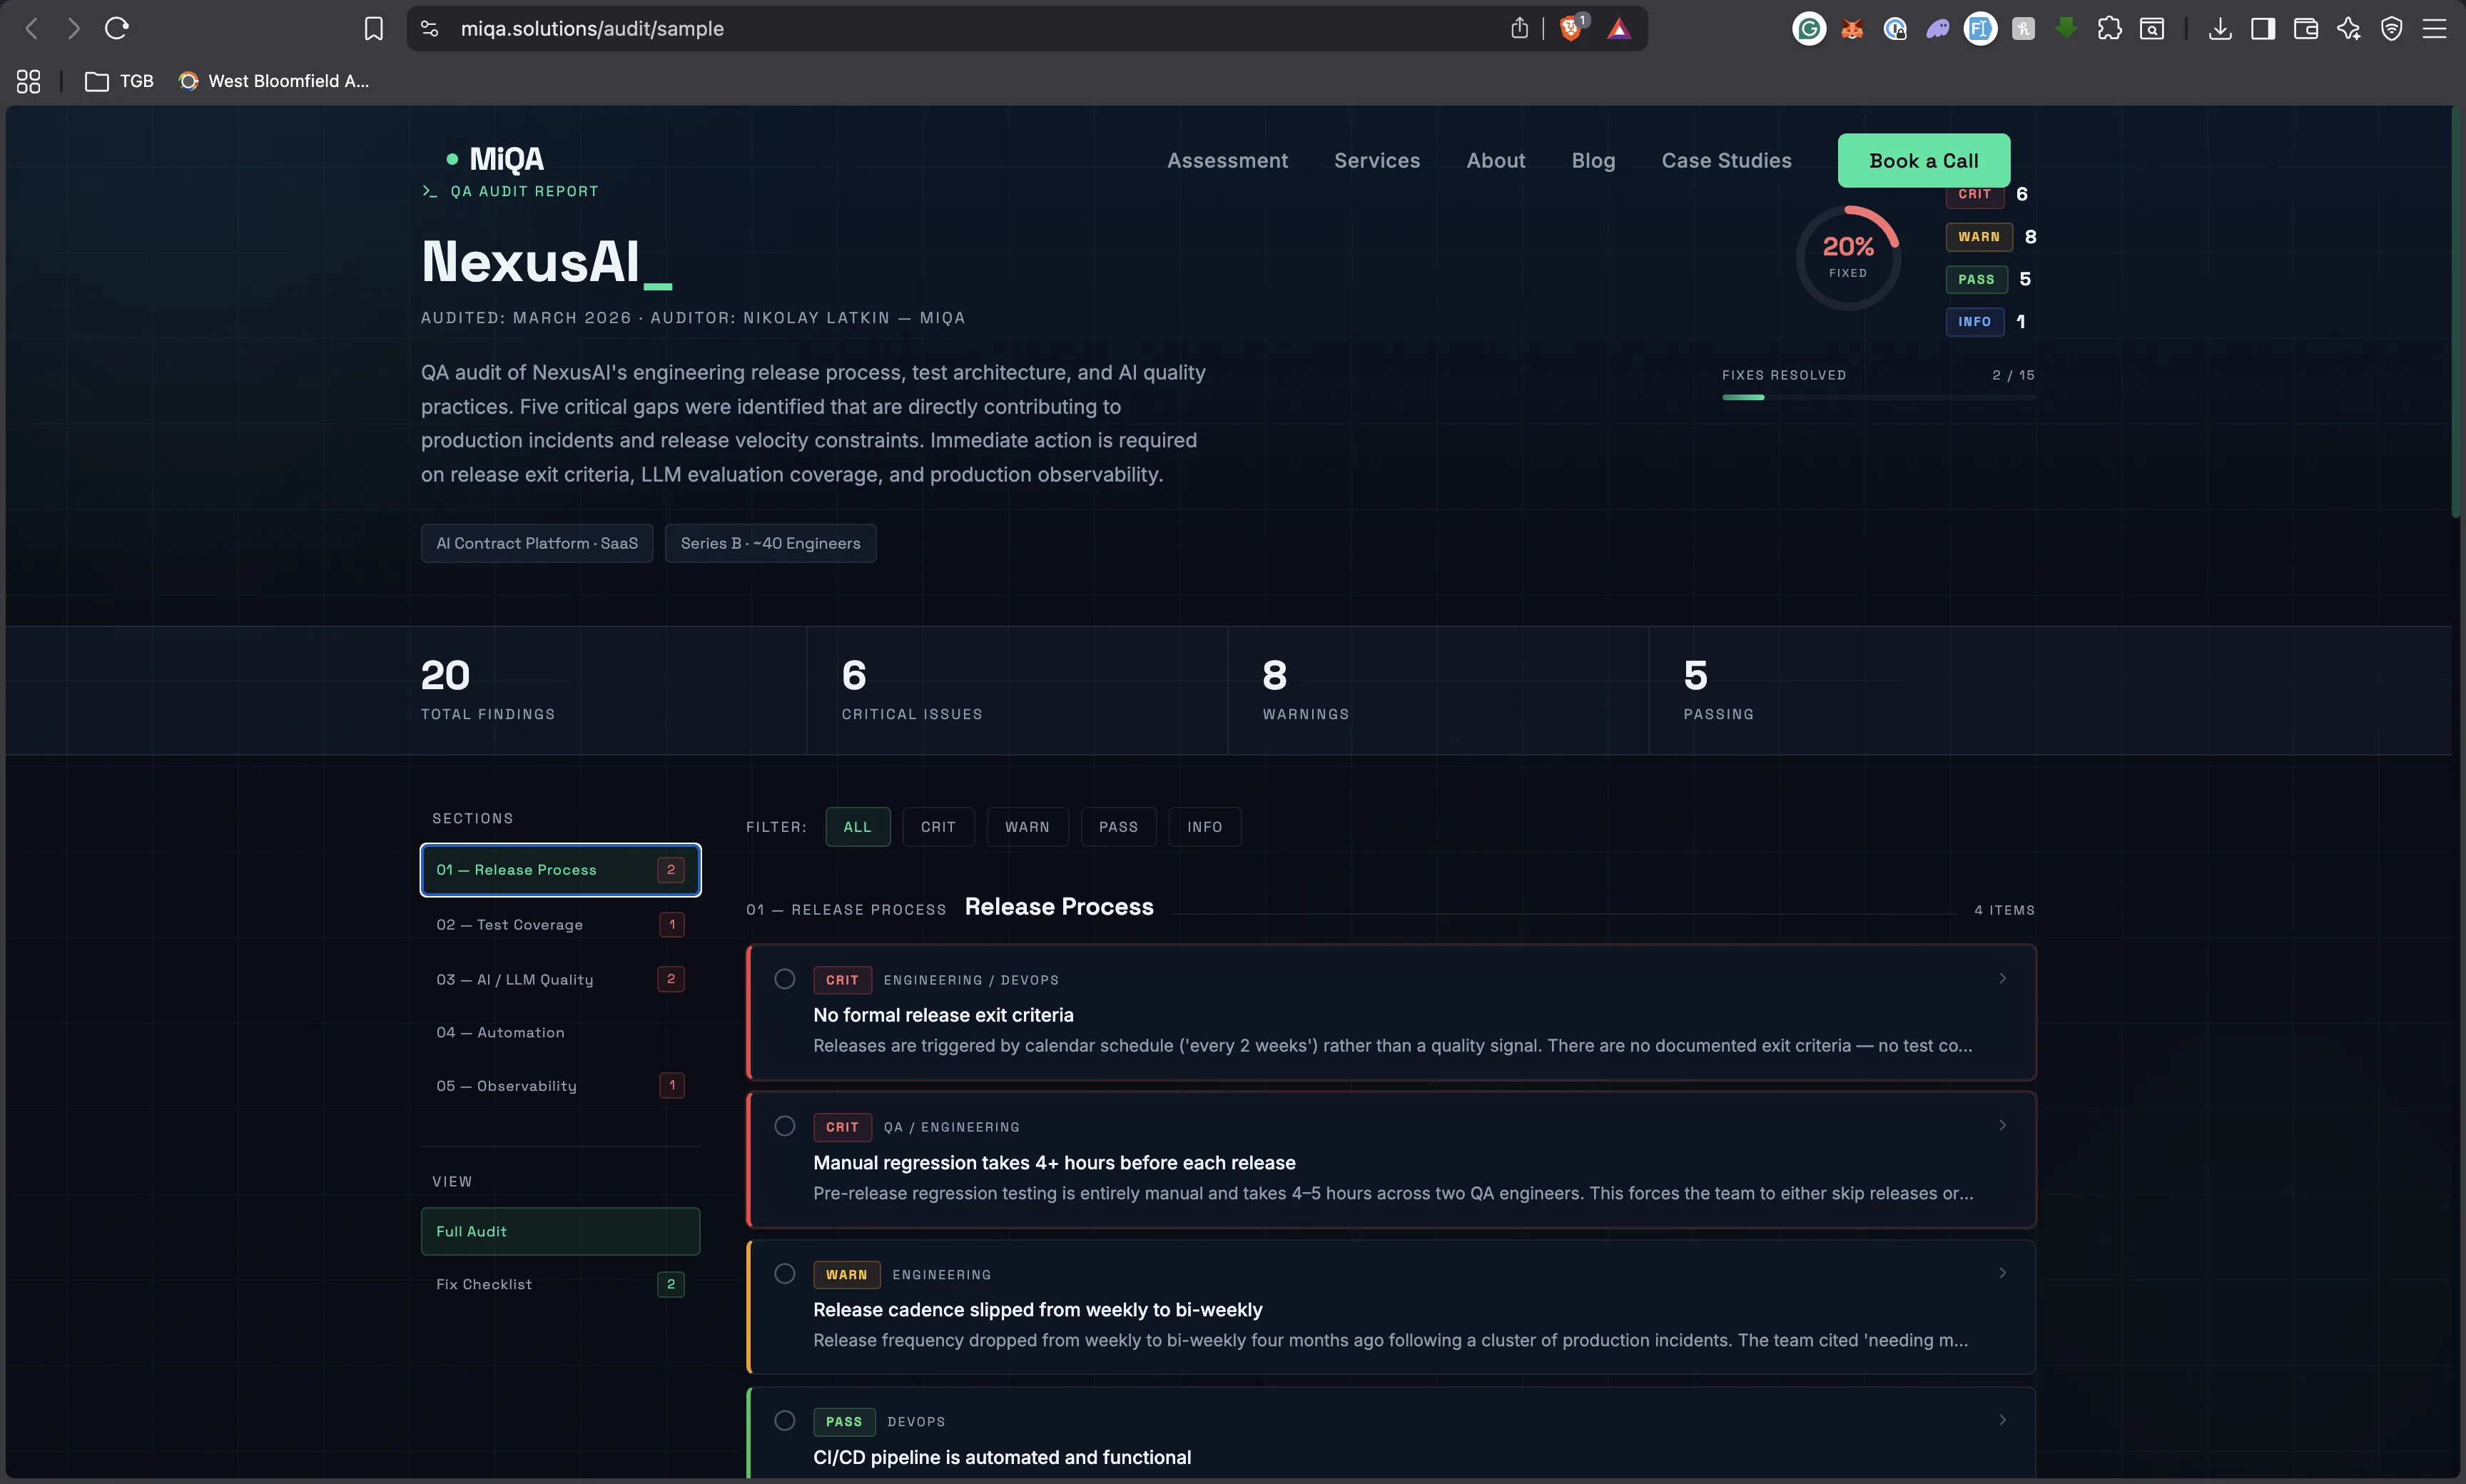
Instead of a static report, we delivered an interactive web dashboard. The client's engineering team could filter findings by severity, read the full context for each issue, and track fixes in real time.
Filter by Severity
Sort all findings by CRIT, WARN, PASS, or INFO instantly.
Fix Checklist
Prioritized action items with progress saved in the browser.
Section Navigation
Scroll-spy sidebar for fast navigation across audit sections.
Actionable Fixes
Every finding includes a specific, implementable fix recommendation.
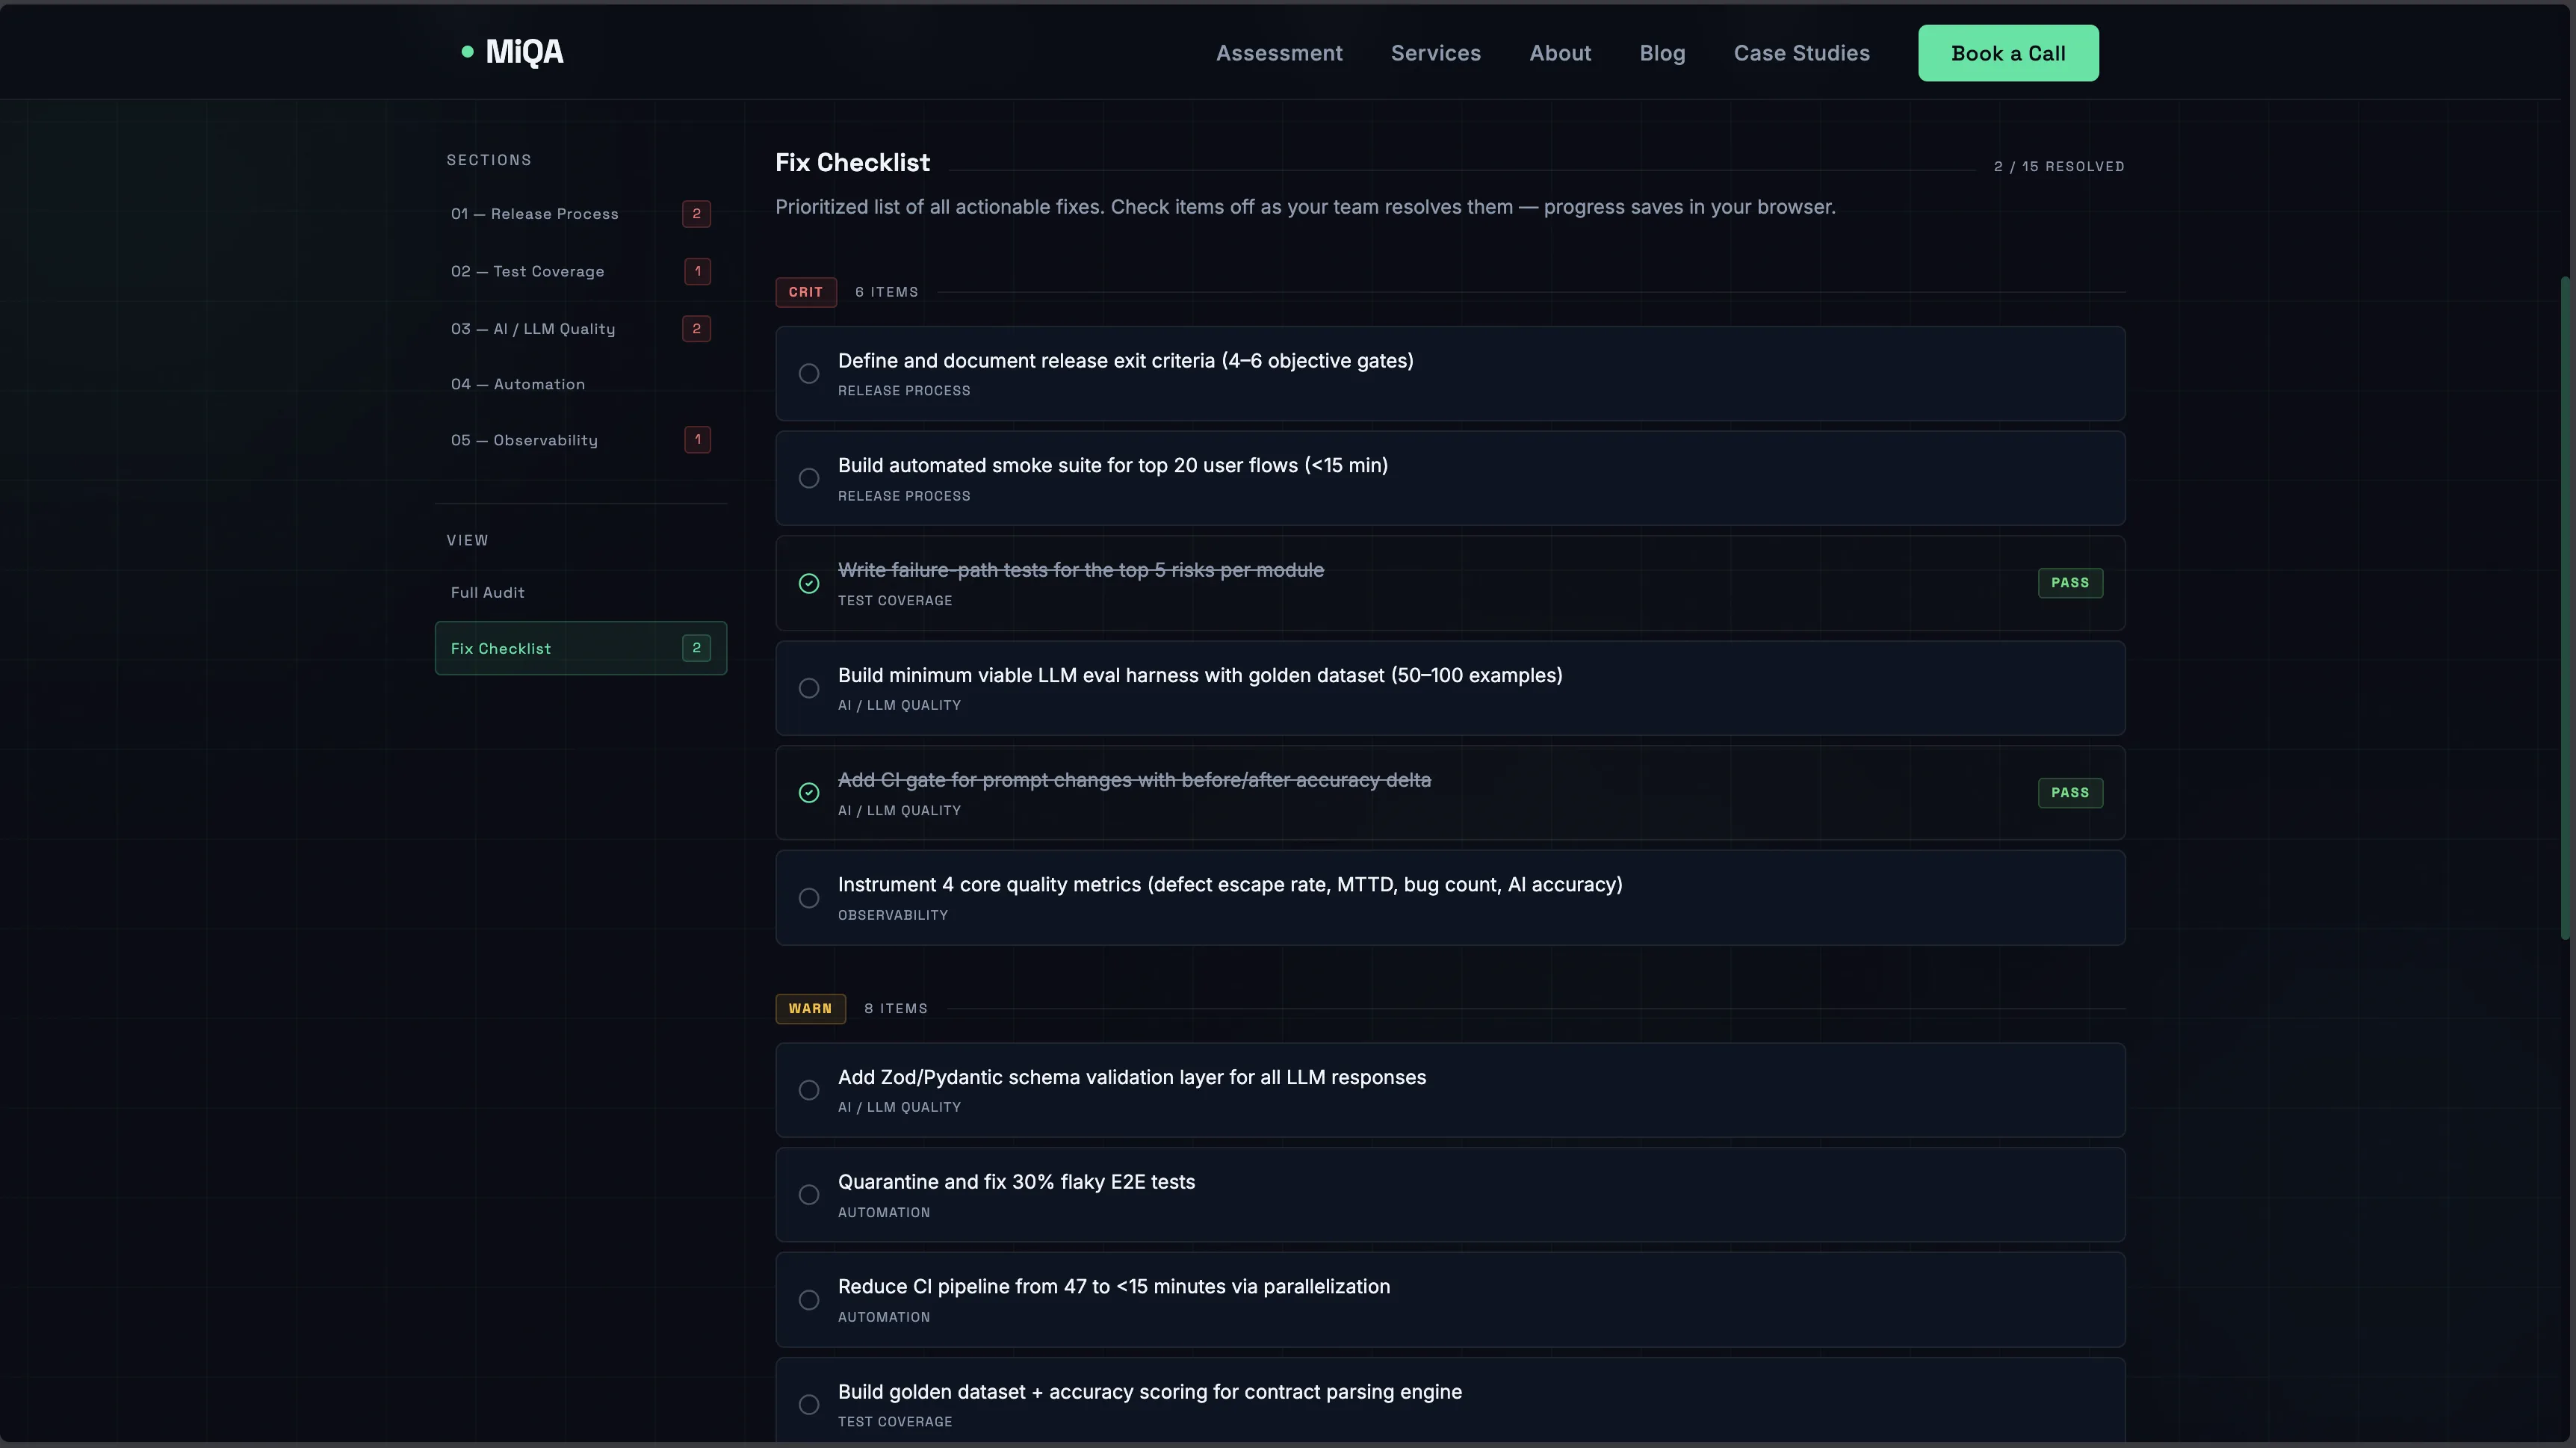
↑ The Fix Checklist — a prioritized backlog your team can act on immediately
"The audit found a database security issue we had no idea existed. If that had gone live, it would have been a serious problem for our users and our launch. The interactive format made it easy to hand off directly to the team."
Get the same level of analysis for your product.
MiQA covers your full stack — UI, API, security, SEO, and database policies — with senior QA leadership and, where needed, managed execution. You get an interactive dashboard your team can act on immediately, not a PDF that sits in a folder.